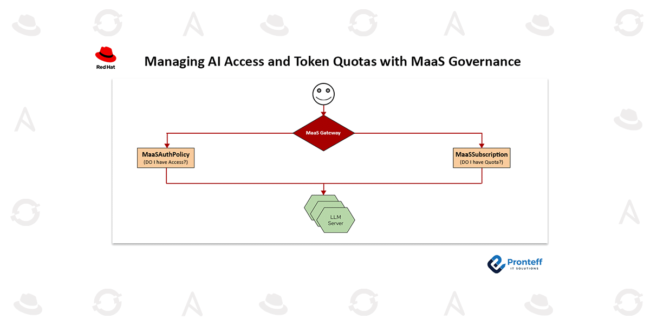
Scaling Enterprise Agentic AI: Building a Governed Evaluation Framework with Alquimia and Red Hat OpenShift AI

  Artificial Intelligence ·Agentic AI · Red Hat OpenShift AI · Enterprise AI Scaling Enterprise Agentic AI: Building a Governed Evaluation Framework with Alquimia and Red Hat OpenShift AI Discover how Alquimia, Gaussia, EvalHub, and MLflow work together with Red Hat OpenShift AI to automate AI agent evaluation, improve behavioral consistency, and establish enterprise- grade…
Opening the Black Box: Profiling a Secured Agentic Pipeline on Red Hat OpenShift AI

  Artificial Intelligence · OpenShift AI · Performance Engineering Opening the Black Box: Profiling a Secured Agentic Pipeline on Red Hat OpenShift AI Understand where latency and resource consumption occur in a secured agentic AI workflow, and learn why profiling the complete pipeline—not only the model—is essential for performance and capacity planning. ━━━━   As…

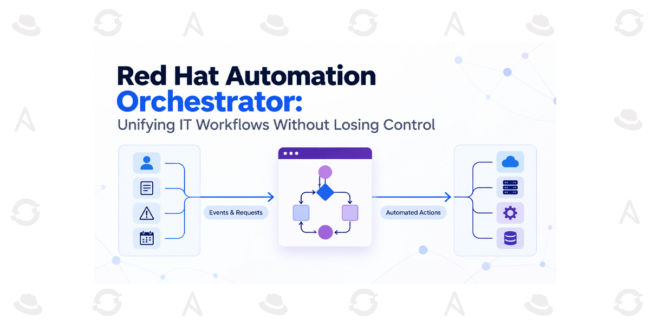
Red Hat Automation Orchestrator: Unifying IT Workflows Without Losing Control

Red Hat Automation Orchestrator: Unifying IT Workflows Without Losing Control

Red Hat Automation Orchestrator: Unifying IT Workflows Without Losing Control How to connect existing Ansible automation, event-driven triggers, and AI-assisted decisions into workflows that remain governable when production gets complicated. A patch is ready. The affected systems have been identified. But before the change can run, someone must verify the risk, obtain approval, coordinate multiple…

OpenShift 4.22 EVPN: Connecting User-Defined Networks to Enterprise Fabrics

OpenShift 4.22 EVPN: Connecting User-Defined Networks to Enterprise Fabrics

OpenShift 4.22 EVPN: Connecting User-Defined Networks to Enterprise Fabrics A practical architecture view of BGP EVPN for primary ClusterUserDefinedNetworks—and the routing, isolation, and operational questions to resolve before production. A workload can keep its IP address after a move and still lose connectivity. The reason is simple: an address is only useful when the surrounding…

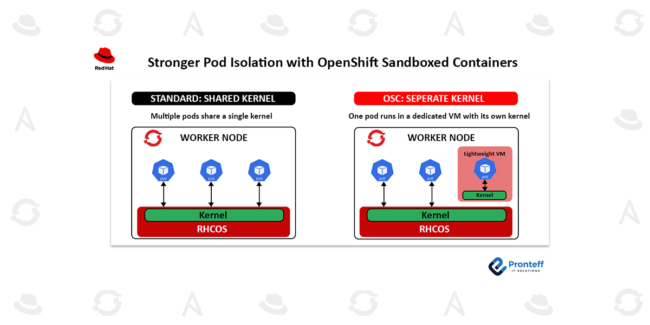
Stronger Pod Isolation with OpenShift Sandboxed Containers

Stronger Pod Isolation with OpenShift Sandboxed Containers

Stronger Pod Isolation with OpenShift Sandboxed Containers In this blog, we will learn about stronger pod isolation with OpenShift sandboxed containers. Containerized applications running on Red Hat OpenShift already benefit from multiple built-in security mechanisms. Security Context Constraints (SCCs) control the permissions available to pods, SELinux provides mandatory access control, cgroups regulate CPU and memory…